强化安全审计工作分级闭环管理 提升安全防护水平
2019-08-19 01:36:56赖振杰
中小企业管理与科技·中旬刊
2019年6期
赖振杰
【摘 要】在某省移动公司业务支撑系统迅速发展的同时,数据信息安全问题也逐渐成为制约系统发展、威胁数据可靠性的第一隐患。某省移动公司针对现状进行实践和创新,提出以业务和风险为中心来推进信息安全建设,根据SOX(《萨班斯法案》)的审计要求,制定分级审计的方案,即审计工作的分级负责、协同处理,审计任务由操作者责任单位的审计人员负责执行,保障审计任务处理的确定性、及时性。
【Abstract】With the rapid development of the business support system of a mobile company in a certain province, data information security has gradually become the first hidden danger that restricts the development of the system and threatens the reliability of data. According to the current situation to practice and innovate, a mobile company in a province proposes to promote information security construction by focusing on business and risk. According to the auditing requirements of SOX (sarbanes act), a hierarchical auditing scheme is formulated, namely, the hierarchical responsibility and cooperative processing of audit work. Audit tasks are performed by the auditors of the operator's responsibility unit to ensure the certainty and timeliness of the handling of audit tasks.
【关键词】电信运营企业;信息安全管理;分级审计
【Keywords】telecommunication operation enterprise; information security management; hierarchical auditing
【中图分类号】F239 【文献标志码】A 【文章编号】1673-1069(2019)06-0022-02
1 建设背景
近年来,移动业务迅速发展,业务数据量激增,数据安全问题也日益突出,对信息安全的审计要求也在逐步提升。为督促落实各项信息安全管理办法、技术规范,根据《萨班斯法案》的审计要求,结合实际,制定分级审计的方案,即审计工作的分级负责、协同处理,审计任务由操作者责任单位的审计人员负责执行,保障审计任务处理的准确性、及时性。
2 常态化的分级审计模式
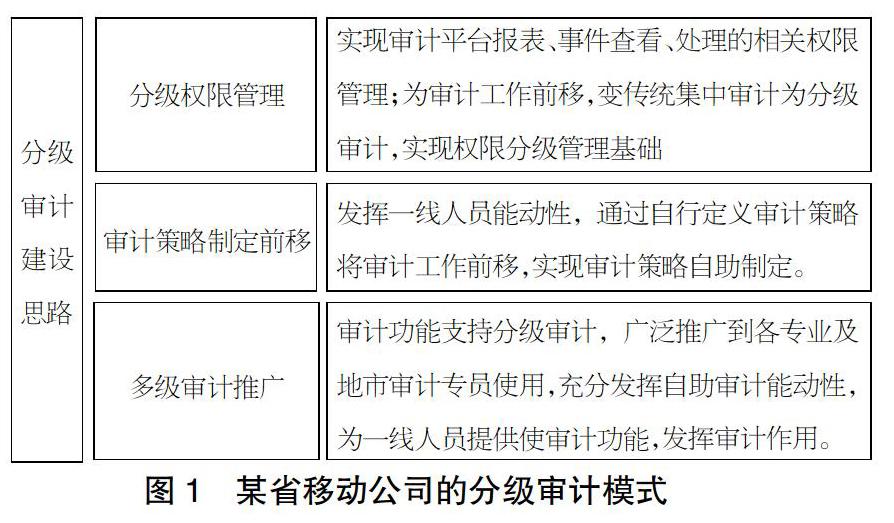
某省移动公司的分级审计模式基于4A审计平台进行建设,主要包括审计系统的分级权限管理、审计策略制定前移、分级审计工作推广三方面的工作。(图1)
基于分级审计系统建立了以审计任务、审计职责为核心的分级审计责任制,从审计职责明确化、审计工作常态化、审计体系层次化三个方面来规范该省的分析审计工作。
①审计职责明确化:合理划分审计权限、数据范围,使各级审计人员执行职責范围内的审计任务。……
登录APP查看全文