基于LSTM-AutoEncoder的水平越权漏洞检测
2020-07-09 22:03:57李帅华孙庆贺赵明宇
现代信息科技
2020年23期
李帅华 孙庆贺 赵明宇


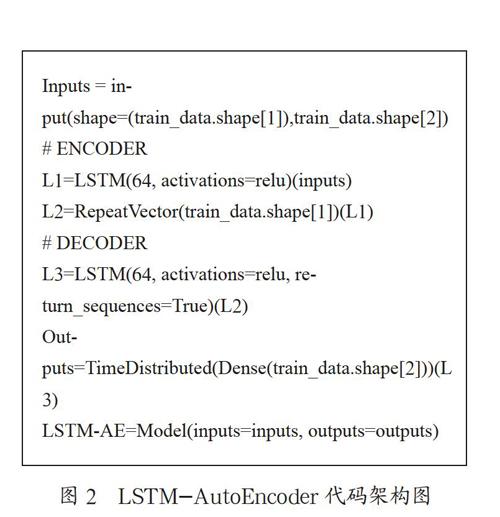
摘 要:针对水平越权检测过程中,因无法识别越权场景页面带来的检测误报问题,提出了一种基于深度学习的LSTM-AutoEncoder无监督预测模型。该模型利用长短时记忆网络构建自动编码器,提取水平越权场景页面响应数据的文本特征并将其重建还原,统计还原结果与原始页面响应的误差,并根据未知页面的误差阈值判断水平越权的检测结果是否为误报。通过与One-Class SVM和AutoEncoder两种算法的比较,在真实业务数据下进行模型效果测试其有效性,为企业网络业务安全提供了保障。
关键词:LSTM-AutoEncoder模型;水平越权;深度学习;网络安全;漏洞检测
中图分类号:TP393.08 文献标识码:A 文章编号:2096-4706(2020)23-0153-07
Horizontal Privilege Escalation Vulnerability Detection Based on
LSTM-AutoEncoder
LI Shuaihua,SUN Qinghe,ZHAO Mingyu
(State Grid Electric Vehicle Service Co.,Ltd.,Beijing 100053,China)
Abstract:Aiming at the problem of detecting false positives caused by ones inability to identify the page of the unauthorized scene in the horizon privilege escalation detection process,an unsupervised prediction model of LSTM-AutoEncoder based on deep learning is proposed. This model uses LSTM(Long Short-Term Memory)to construct an autoencoder,which extracts the response datas text features of the horizontal privilege escalation scene page and reconstructs it. Then calculates the error between the restored result and the original page response,and judges whether the horizontal privilege escalation detection result is a false positive based on the error threshold of the unknown page. By comparing the two algorithms of One-Class SVM and AutoEncoder,the effectiveness of the model is tested under real business data,which provides a guarantee for the security of corporate network services.
Keywords:LSTM-AutoEncoder model;horizontal privilege escalation;deep learning;cyber security;vulnerability detection
0 引 言
越权漏洞属于业务逻辑漏洞中的一种,在目前的Web应用中十分常见。水平越权是越权漏洞中的一种,它是指相同权限的用户可以通过修改参数变量等方式查询、修改、删除、添加他人信息,以实现非法行为。当黑客对越权漏洞进行利用时,由于其攻擊行为与正常用户请求无异,且不包含敏感字符与特殊字符,很难被防御软件监控处理。因此,如何能够对水平越权漏洞进行检测,及时修复缺陷漏洞以避免损失显得尤为重要。
近年来,在针对权限提升的防御控制方法上,已经有很多研究工作开展实施[1-5]。在企业实际业务生产过程中,不仅要增强代码开发人员的安全开发意识和代码规范,还需要对即将上线的Web应用有着良好的安全检测。对于特权提升漏洞的检测有如下相关研究:Sun等人提出了利用静态检查的方法来检测Web应用中的逻辑漏洞,通过源码构建不同权限访问者的站点地图,来判断是否存在越权行为[6]。……
登录APP查看全文
猜你喜欢
大灰狼画报·益智版(2024年3期)2024-12-09 00:00:00
保健医苑(2022年1期)2022-08-30 08:39:14
美与时代·美术学刊(2022年3期)2022-04-27 01:18:15
人大建设(2019年12期)2019-05-21 02:55:32
商用汽车(2016年11期)2016-12-19 01:20:16
商用汽车(2016年6期)2016-06-29 09:18:54
商用汽车(2016年4期)2016-05-09 01:23:12
创业家(2015年5期)2015-02-27 07:53:25
电脑爱好者(2011年11期)2011-06-22 08:20:18
中国火炬(2010年8期)2010-07-25 11:34:30